Platform Engineering ·
gh-secure: A Two-Minute Security Baseline for Open Source Repositories
A practical review of GitHub Security Lab's gh-secure CLI extension, what it configures, where it helps, and what maintainers still need to own.
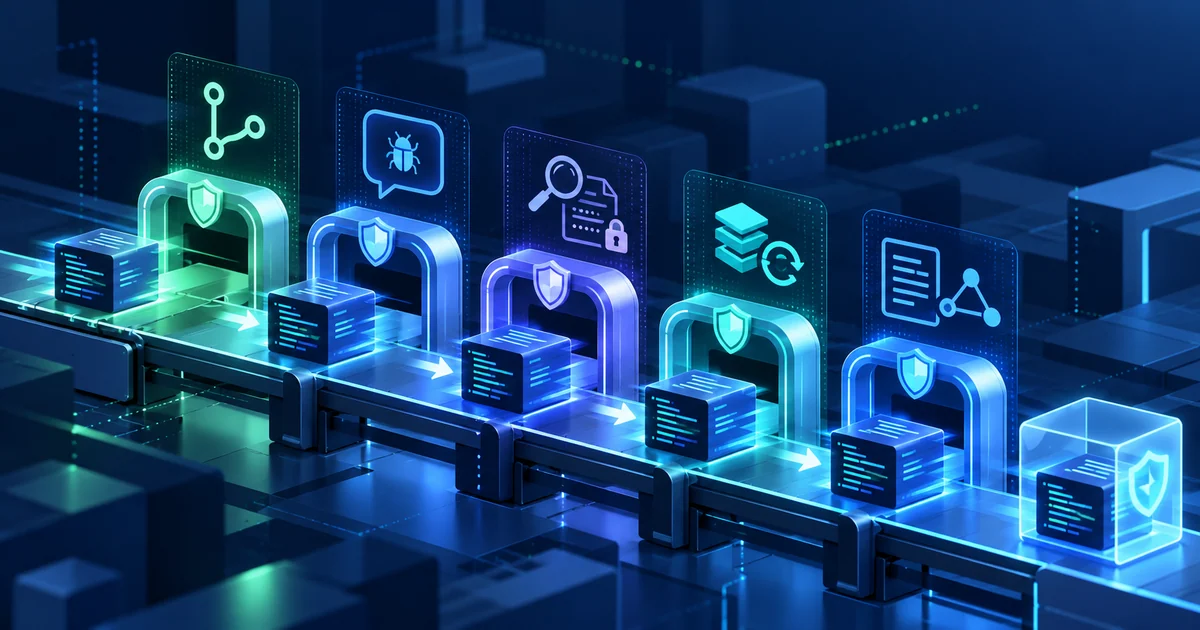
Security guidance is easy to agree with and surprisingly easy to postpone. A maintainer may know that a repository should protect its default branch, scan for leaked credentials, monitor dependencies and offer a private reporting channel. The harder part is translating that checklist into the correct repository settings without overlooking a control or creating conflicting rules.
gh-secure is a GitHub CLI extension from GitHub Security Lab designed to close that setup gap for public repositories. Its promise is deliberately narrow: inspect a repository and enable a practical baseline of GitHub security features in roughly two minutes. That makes it useful as bootstrap automation, especially for open-source maintainers who do not operate a dedicated application-security program.
What the tool configures
The extension covers five areas:
- Branch protection limits unwanted changes to the default branch. Before applying legacy branch protection, the tool checks for active repository rulesets and warns about possible overlap.
- Private vulnerability reporting and a security policy give researchers a non-public route for reporting a vulnerability before maintainers have prepared a fix.
- Secret scanning with push protection detects supported credentials and attempts to stop new secrets from entering repository history.
- Dependabot identifies dependencies with known vulnerabilities and can create pull requests for available fixes.
- Code scanning with CodeQL analyzes supported languages for vulnerability patterns and reports findings on pushes and pull requests.
GitHub describes these capabilities as free for open-source projects. Availability still depends on the repository, its languages, organization policy and the permissions of the person running the command. The project documentation requires an authenticated GitHub CLI session and admin or maintainer access; organization repositories may also require the admin:org OAuth scope.
A sensible first run
Installation follows the normal GitHub CLI extension model:
gh extension install GitHubSecurityLab/gh-secure
I would not begin with the unattended command on an unfamiliar repository. Start by checking the current state and previewing the proposed changes:
gh secure status --repo owner/repository
gh secure --repo owner/repository --dry-run
Then use interactive mode to examine each control:
gh secure --repo owner/repository
Once the behavior is understood, gh secure --yes enables all selected features without confirmation. Individual controls can also be chosen by name, for example gh secure branch-protection dependabot, which is helpful when an organization already manages some settings centrally.
This sequence matters because repository security settings change contributor workflows. Branch protection may prevent direct pushes. Push protection can reject commits containing detected credentials. Dependabot adds a pull-request stream that someone must triage. Code scanning creates findings that need ownership and a response policy. Automation makes configuration fast; it does not make these consequences disappear.
Where gh-secure is strongest
The tool turns a fragmented settings exercise into one repeatable entry point. That has three practical advantages.
First, it reduces omission risk. A maintainer is less likely to enable dependency alerts while forgetting private vulnerability reporting or secret scanning. Second, status and --dry-run make the intended state reviewable before mutation. Third, selective feature names allow the extension to complement existing governance rather than insisting on an all-or-nothing model.
The project also documents use through AI assistants that can invoke the tool. That can make discovery conversational—ask what is missing, request an explanation, then apply selected changes—but the security boundary remains the authenticated gh session. An assistant inherits the effective token permissions, so dry runs, least-privilege credentials and explicit human review still matter.
What the tool does not solve
Enabling controls is the start of an operating model, not the end of one.
- Alerts need owners. Dependabot, secret-scanning and CodeQL findings need triage expectations, severity rules and escalation paths.
- A passing scan is not proof of safety. CodeQL covers supported languages and modeled vulnerability classes; it cannot establish that the design, authorization model or business logic is secure.
- Branch governance is contextual. A legacy protection rule may duplicate or conflict with organization rulesets. The tool warns about active rulesets, but maintainers must decide which policy should be authoritative.
- Detected secrets still require incident response. Removing a credential from a commit does not invalidate it. A leaked secret must be revoked, rotated and investigated.
- Dependency pull requests still require engineering judgment. Updates can introduce breaking changes or operational risk even when they remediate a vulnerability.
- Private reporting needs a human response. Opening a channel is useful only if someone monitors it and communicates with reporters.
The repository documentation is appropriately clear on the larger point: no configuration tool can guarantee complete security. gh-secure raises the floor; it does not replace threat modeling, secure design, review, testing or incident preparedness.
A lightweight adoption checklist
For an engineering leader or maintainer introducing the extension, I would use this sequence:
- Confirm the target repository and the scopes attached to the current GitHub CLI session.
- Run
gh secure statusand keep the output with the review record. - Run
--dry-run; compare the proposed changes with organization rulesets and compliance requirements. - Enable one or more missing controls interactively.
- Verify the resulting repository settings directly in GitHub.
- Assign owners for security alerts, dependency updates and private reports.
- Test the workflow with a harmless example, such as a protected-branch change or a test repository containing a recognized dummy credential.
- Recheck status periodically and after repository transfers, policy changes or major platform migrations.
The engineering-leadership view
The most valuable thing about gh-secure is not that it introduces a new security technique. It packages five established controls into a small, inspectable workflow. That is exactly the kind of automation platform teams should favor: narrow enough to understand, safe to preview, selective when local policy differs, and explicit about its limits.
For an open-source project with little security configuration, the extension offers a strong first action. For a mature organization, it can serve as a baseline checker or onboarding aid, provided central rulesets and ownership models remain authoritative. In both cases, the right success measure is not whether the command completed. It is whether the repository now has working guardrails and a team prepared to respond to what those guardrails find.
Source: GitHub Security Lab — gh-secure repository and usage documentation.